
AI·News & analysis
Grok Build apps left open to anyone, including SpaceXSI's own
Security firm Claroc found more than 35,000 apps made with SpaceXSI's Grok Build that anyone could open with no sign-in. Some held medical exams, rosters and the company's own sales plans.

Tide
Wave
Sci-fi
3/10
Reality
In your hands
A robot builds your app in minutes, then leaves the door open.How we rate
Security firm Claroc found 35,578 of 37,571 online Grok Build apps, or 94.7%, open to anyone with no sign-in, including 24 built by SpaceXSI and X staff.
The exposed data included medical exams, staff rosters and confidential sales plans. The cause is a link design that puts the random part in the hostname, where public DNS records can reveal it. SpaceXSI removed its own 24 apps, and Claroc is notifying the other affected organizations.
What to know
- Claroc listed 43,601 Grok Build app addresses under grok.me. Of 37,571 still online, 35,578 (94.7%) opened for anyone with no sign-in.
- 24 of the open apps were built by SpaceXSI and X staff, with a confidential onboarding plan and a map of 594 sales accounts.
- The cause is the link design: the random part sits in the hostname, so public DNS records reveal it.
- SpaceXSI took down its own 24 apps within hours of questions, but the other users' apps stayed open at publication.
Security firm Claroc found that more than 35,000 apps made with Grok Build could be opened by anyone who found their address. Some held business plans, staff lists and medical results. Some belonged to SpaceXSI, the company that makes Grok.
That is the news. Now the question: how do apps with random web addresses end up on a list that anyone can search?
First, what is Grok Build?
Grok Build is a vibe-coding agent from SpaceXSI, the name of the now-merged SpaceX and xAI. Vibe coding means you describe what you want in everyday words, and the AI writes the software for you. You can have a working app in minutes.
When you publish one, it gets its own address under the grok.me domain. Anyone with that address can open the app, as long as the sharing setting allows it. Most of these apps are games, landing pages and calculators.
But people also use tools like this for work. A sales lead builds a quick team tracker. A hospital manager builds a staff board. Nobody asks IT first, because it takes ten minutes.
How many apps were open?
Claroc listed 43,601 app addresses under grok.me. Of the 37,571 still online, 35,578 opened for anyone with no sign-in. That is 94.7 percent. Only 1,993 returned an access-denied error.
Claroc estimated that about one in 10 open apps held sensitive business or personal data. It put the number of apps with private data at roughly 650 to 800.
- Addresses found: 43,601 under grok.me.
- Still online: 37,571.
- Open to anyone: 35,578, or 94.7%.
- Likely holding private data: about 650 to 800.
Most of the exposed apps were harmless, but the few that were not held real people's names, health details and company secrets.
What was inside the apps?
Claroc confirmed a number of cases by hand. A hospital group's roster listed more than 3,500 employees. An intensive care briefing for one patient showed lab results and ventilator status. A fire department's live shift board listed badge numbers.
One contractor's timesheet app had code that held 18 employee accounts with passwords in plain text. Claroc also identified 30 organizations with internal data in open apps. Of those, 26 had more than 1,000 employees and six were in the Fortune 500. Claroc did not name them.
A longer list of examples was shared with reporters:
- Tesla: a service-center scorecard naming 22 technicians, with productivity and bonus status.
- A Peruvian construction company: a health dashboard with 3,784 worker medical exams.
- A US Navy ship engineering contractor: a roster of 108 people on a logistics support contract.
- A Norwegian-Finnish aerospace and defense group: a load board for an explosives building at a US plant.
- An auto transport company: a quote desk with about 4,000 vehicle-transport orders, prices and margins.
- A US home construction company: a call sheet with about 583 home-buyer prospects, budgets and financing notes.
Whose data was it, besides customers'?
SpaceXSI's own. Claroc found 24 open apps built by SpaceXSI and X staff. They included an onboarding plan, marked confidential, for a new member of the enterprise sales team. It listed internal system addresses, the team's tools and 19 internal chat channels.
There was also a map of 594 strategic sales accounts and their pipeline. Other apps held eight X advertising proposals and media plans, one to a US federal agency and marked confidential. Four live advertiser boards showed campaign spend, and there were campaign reports for advertisers in Brazil, Japan, Korea and Thailand.
"We were shocked," wrote Asaf Aprozper, Claroc's co-founder and chief technology officer. "The company that makes Grok had its own internal material open to anyone holding the link."
In real life Imagine a team builds a quick tracker for sales accounts, then shares it by link in chat. The link is long and random, so it feels private. In fact, it was in a public list from the first time anyone opened it.
Why could anyone find the links?
Here is the technical heart of it. Grok gives each app an address like four random words followed by grok.me. The random words are meant to make the address hard to guess. This idea is called capability-based access: whoever holds the link is allowed in.
Google Docs uses the same idea, but it puts the random code after the domain, in the path. Grok put it before, in the hostname.
That matters because of DNS, the internet's phone book. Every time someone opens an address, a DNS lookup turns the name into a machine address. Passive DNS services collect these lookups into databases that anyone with an account can search by pattern. A name in the hostname lands in that database. A path never does.
- Grok Build: the random part is in the hostname, so passive DNS records it.
- Claude's published artifacts, ChatGPT's shared conversations and Gemini's shares: the random part is in the path, so DNS never sees it.
The catch: Claroc says Lovable, Replit, Bolt and other app builders also give each app its own hostname, so the same records can expose them. It reports that Grok is where it found by far the most sensitive company data.
Was "Anyone with the link" the default?
This is where the two sides differ. In Claroc's paid account, the publish panel offered "Anyone with the link", "Invited users" and "Only you", with the first already selected. Aprozper said tests over the past week showed that Grok sets links to "Anyone with the link" by default.
A representative of Cursor, the AI coding company SpaceXSI recently acquired, said Grok Build apps "are private by default and nothing goes public unless the creator chooses to share it." The representative also said competing coding agents from ChatGPT, Lovable and Bolt let users make shareable links too. SpaceXSI also told a reporter that publishing takes several clicks and a legal disclaimer, and that employee accounts default to "Only you".
Claroc says its tests contradict the claim: in each case, users had to change "Anyone with the link" to one of the other two options. The representative did not answer follow-up questions, including why the company removed its own apps.
What happened after the report?
Claroc reported the problem to SpaceXSI through the address in the company's security.txt file on Nov. 8. It sent details of the other 22 staff apps on Nov. 9. When nobody replied, a Claroc official tagged Elon Musk and a Grok manager on X.
All 24 SpaceXSI apps were still exposed on Monday evening. SpaceXSI began removing the links within a few hours of reporters emailing questions. By Tuesday, they returned an "app not found" error.
The apps of other users were still open at publication. Claroc says SpaceXSI had not said it would contact those owners, so it began notifying them itself. It had emailed three by publication. Aprozper said the luxury cruise company's security chief pulled in the whole security team right away and began working to contain the exposure.
Claroc also asked SpaceXSI to make four changes:
- One host: serve apps under a path on a single host.
- Team sharing: add an organization-only option.
- Safer default: make "Only you" the default setting.
- A warning: warn when an app has a database but no sign-in.
Is this the first Grok Build privacy scare?
No. In July 2026, a researcher named Cereblab found that the Grok Build command-line tool packaged users' whole code repositories, including Git history and committed secrets, and uploaded them to company cloud storage. Elon Musk said all stored data would be deleted.
SpaceX then published the tool's code as open source in a single commit, around 844,000 lines of Rust. It said it had turned off data retention by default from July 12 and invited researchers to report problems through a bug bounty program paying $100 to $20,000. That earlier case was about a tool on developers' computers. This one is about apps that people publish to the web.
Claroc also tested its own app. In a team app where Grok added Google and X sign-in, the code added whoever signed in to the team before checking membership. An uninvited Google account could read, edit and delete records. Claroc says it ran write tests only on its own apps.
What it means for you
- If you build apps with an AI tool: open the sharing settings and pick "Only you" or "Invited users" unless the app is meant for the public.
- Never put secrets in a quick app: passwords, patient data and staff IDs do not belong in something built in ten minutes.
- If you work for a company: ask what AI-built tools your team has published. IT may not know they exist.
- If your data may be in one: ask your employer. Claroc is notifying organizations it identified.
The bottom line
AI can now build an app in minutes, and it can publish it just as fast. The link design turned "hard to guess" into "easy to look up", and thousands of people did not know.
The fix for users is one setting. The fix for the platform is where the random part of the address lives. Until then, treat every published app as public unless you chose otherwise.
Key facts
- Apps listed
- 43,601 addresses under grok.me
- Open with no sign-in
- 35,578 of 37,571 online (94.7%)
- SpaceXSI apps exposed
- 24, now returning 'app not found'
- Found by
- Security firm Claroc, published Nov. 10, 2026
Got questions?
Quick answers, plain wordsWhat is Grok Build?
Grok Build is SpaceXSI's coding agent. You describe an app in plain words or by voice, and the AI writes it. You can then publish the app at its own web address under grok.me.
What exactly leaked?
Data stored inside apps that people built and published. Claroc found business plans, ad proposals, staff rosters with names and ID numbers, medical exam results and, in one case, passwords stored as plain text.
Who found the problem?
Claroc, a security firm. Its co-founder and chief technology officer, Asaf Aprozper, led the research and published the findings on Tuesday, Nov. 10, 2026.
How many apps were open?
Claroc found 43,601 addresses. Of the 37,571 still online, 35,578 opened for anyone, which is 94.7 percent. Only 1,993 returned an access-denied error.
Was SpaceXSI's own data exposed?
Yes. Claroc found 24 open apps built by SpaceXSI and X staff, including a confidential onboarding plan for a sales hire and a sales map of 594 accounts. They now return an 'app not found' error.
Did SpaceXSI respond?
A representative of Cursor, the coding company SpaceXSI recently acquired, said apps are private by default and nothing goes public unless the creator shares it. The representative did not answer follow-up questions.
Is my Grok Build app at risk?
Check its sharing setting. If it says 'Anyone with the link', anyone who finds the address can open it. Switch it to 'Invited users' or 'Only you' unless you want it public.
Why can people find these links if they are random?
The random words come before grok.me, in the hostname. Every visit triggers a DNS lookup, and public databases of those lookups can be searched. Google Docs puts its random code after the domain, where DNS never sees it.
Do other AI app builders have the same issue?
Claroc says Lovable, Replit and Bolt also give each app its own hostname, so the same records can expose them. It reports that Grok is where it found by far the most sensitive company data.
Has Grok Build had privacy problems before?
Yes. In July 2026 a researcher found its command-line tool uploading whole code repositories to company cloud storage. Elon Musk said the uploaded data would be deleted, and the tool was then open-sourced.
SourcesArs Technica
Topics and tagsxAI, grok build, spacexsi, data leak
Related guide
Guide, 10 minHow to use ChatGPT in Chrome, try-on shopping and stay safe from fake GPTsSet up the ChatGPT Chrome extension, use its tab, shopping and try-on tools, and avoid the fake custom GPTs that have been used to spread...Related stories
Claude cracks the 25-year mystery behind the internet's favorite crypto curves
Anthropic says an internal Claude model showed in under half an hour that the NSA's unexplained NIST curve seeds came from a 1990s random number generator and a clock, not a secret passphrase.
OpenAI engineer charged over hidden recording device in executive room
Federal prosecutors say an OpenAI engineer wrapped a tiny recorder in toilet paper and plugged it into a TV in an executive conference room in San Francisco.
Google Play will now install the apps you vibe-code yourself
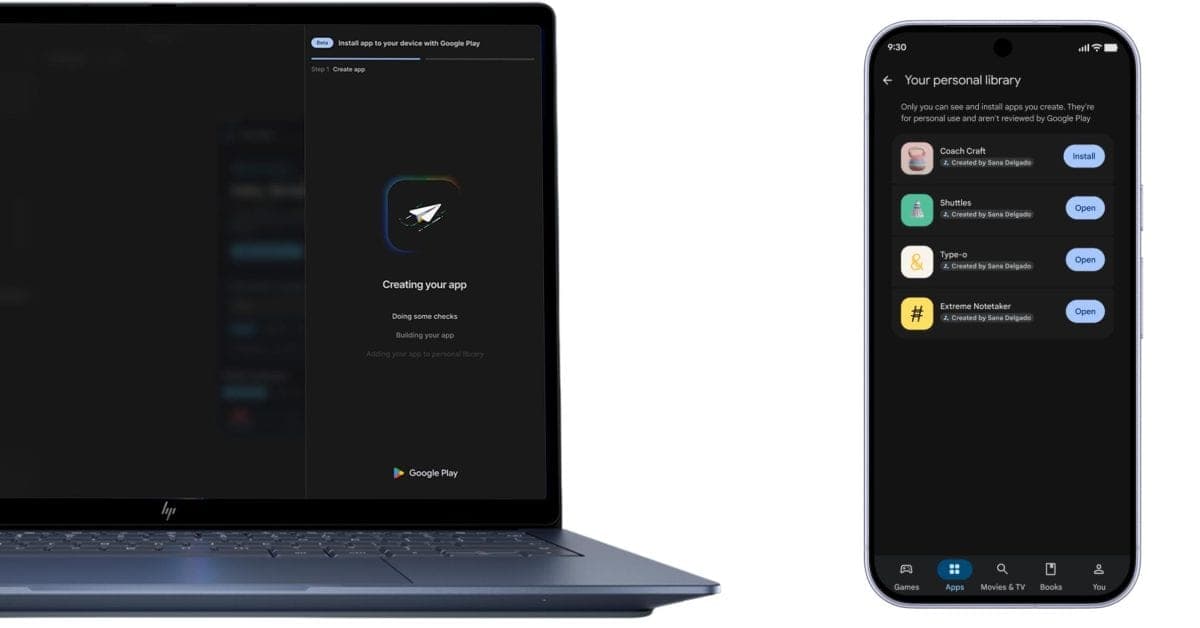
Anyone with a Google account can send an app built with AI in Google AI Studio to a private Play Store library. AI game picks and app comparisons came along too.
More in brief
- FAA lifts a nationwide ground stop after a communications outageNov 14
- Tesla opens Cybercab orders at $29,990, plus $299 a month to drive itNov 14
- Apple Sports adds UFC with live stats for every fight on the cardNov 13
- LangChain raises $300 million at a $3 billion valuation for AI agentsNov 13
- SignDrop, a new Windows zero-day, gives attackers full System rightsNov 13
- Microsoft's AI Frontiers research group is over, says co-founder John LangfordNov 13