
Technology·News & analysis
GMO Internet says hackers posted data stolen from its Onamae cloud desktops
The Japanese company refused an 8 billion yen ransom demand after a breach that may have touched up to 26,739 servers used for automated currency trading. It now says the attacker has posted data online.
Tide
Ripple
Sci-fi
3/10
Reality
In your hands
A cloud computer that trades currencies while its owner sleeps.How we rate
GMO Internet says an attacker who broke into its Onamae Desktop Cloud service has posted data linked to the company and its customers.
Up to 26,739 servers used for automated currency trading may be affected, and some customers reported unauthorized trades. GMO refuses to pay an 8 billion yen ransom demand and is checking whether the leaked data is real.
What to know
- GMO Internet says an attacker broke into its Onamae Desktop Cloud service and may have installed malicious programs on up to 26,739 customer servers.
- On October 27 the company said the attacker had posted information that appears linked to the company and its customers. GMO is still checking whether it is genuine.
- The attacker demanded about 8 billion yen, roughly $50 million. GMO says it will not pay and will give each customer 5,000 yen, about $30.
- GMO says payment details were not exposed, but trading-account logins stored on the servers may have been, and some customers reported unauthorized trades.
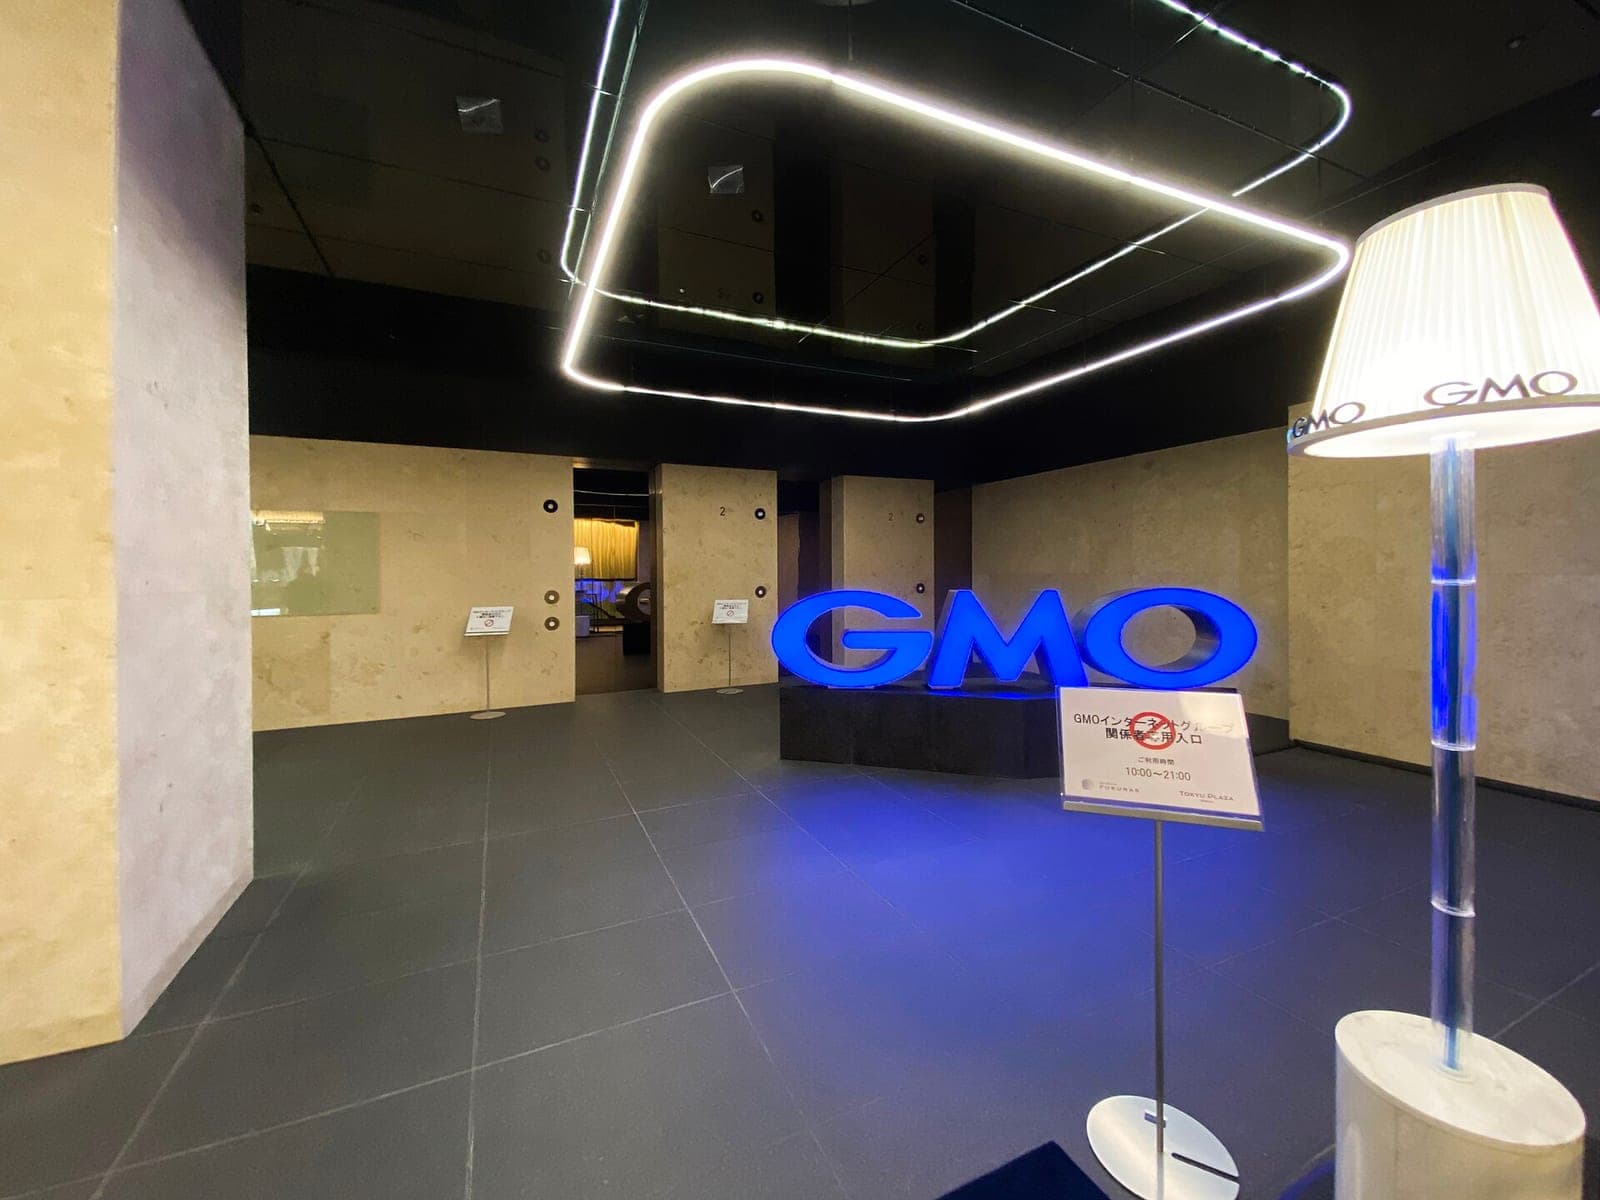
Japanese internet company GMO Internet is dealing with a data leak. TechCrunch reports that suspected hackers broke into its Onamae cloud desktop service and have now posted information online.
That's the news. Here's what the company has said so far, and what is still unknown.
What is Onamae Desktop Cloud?
It is a service run by GMO Internet, one of Japan's largest domain registrars. A domain registrar is a company that sells website addresses.
What it does: BleepingComputer describes it as a VPS service. A VPS, or virtual private server, is a computer you rent in a data center and control over the internet.
Who uses it: TechCrunch says it provides virtual desktops to financial traders. BleepingComputer says it is advertised for stable automated currency trading, including running the MetaTrader 4 program around the clock.
Why it matters: customers leave trading programs running on these servers, so logins for trading accounts may sit on the machines too.
What happened, step by step?
The timeline comes from TechCrunch, BleepingComputer and the Japanese outlet ASCII.jp.
- October 19: GMO began investigating after inquiries from users, according to ASCII.jp.
- October 20: the company confirmed that an unauthorized third party had installed "malicious programs" in some customers' server environments, BleepingComputer reports.
- October 21: GMO shut down all Desktop Cloud servers starting at 4 a.m. local time. It also got an email from the attackers demanding about 8 billion yen, TechCrunch says.
- October 22: GMO reported the incident to police. It also said customers had reported unauthorized operations on their trading accounts.
- October 24: GMO said it would offer compensation and an alternative service, and seek help from government agencies.
- October 25 and 26: the company began collecting devices from customers to look for malware. On October 26 it warned that the attackers planned to leak customer data and trigger ransomware planted on customer servers.
- October 27: GMO said a suspected attacker had posted information that appeared linked to the company and its customers.
What did the attacker threaten?
Ransomware is malicious software that locks or damages a computer until the victim pays. BleepingComputer says GMO warned that the attackers planned to set off a ransomware payload placed on customer servers earlier in the attack.
The warning: on October 27, GMO asked customers to back up their data, disconnect from the internet, shut down their computers and unplug all cables before noon.
What happened next: BleepingComputer says the attacker appears never to have acted on the threat, because no ransomware was activated on customer machines.
The ransom: the attacker asked for about 8 billion yen, roughly $50 million. GMO says it will not pay.
What is confirmed about the leak?
Not everything is clear yet.
TechCrunch says GMO believes the attacker published information allegedly linked to customers and the business. The contents are still being checked, and the full extent is unclear. BleepingComputer says GMO later confirmed that data belonging to both the company and its customers had been published.
GMO has said payment information, such as credit card details, was not exposed. It says that data is stored on different infrastructure.
The catch: GMO says logins for MetaTrader 4 and MetaTrader 5 and trading-account details may have been exposed or misused. An attacker with those logins could place trades.
What are customers told to do?
GMO's advice is practical, and it comes from the company and the outlets that quote it.
- Change passwords: reset passwords for trading tools and trading accounts. Do it from a device other than the affected server, then log off, ASCII.jp reports.
- Check your account: look at transaction history and balances, and contact your trading provider about anything unfamiliar.
- Rotate secrets: BleepingComputer says anyone who stored passwords or similar secrets on the servers should change them quickly.
- Watch for phishing: phishing means fake messages that trick you into giving up passwords. GMO says it will never ask for a password or credit card number by email or phone.
Trading firms moved too. ASCII.jp reports that OANDA Securities asked customers to change trading-account passwords, use two-factor authentication and review their history. AI Gold Securities said it was strengthening its monitoring for unauthorized logins, trades and withdrawals.
What is GMO doing about it?
Compensation: GMO says it will pay each customer 5,000 yen, about $30, for the inconvenience. It will consider more for people whose information was exposed.
Recovery: BleepingComputer says GMO is working with Trend Micro to recover. It is scanning customer systems for leftover malware and offering equivalent PC replacements to customers harmed by a ransomware attack.
Legal action: GMO asked people and the media not to spread the leaked information. It says it will take legal action against those who do.
Is this connected to the AI hacking tool in the news?
Maybe, but nobody has said so. About a week earlier, GMO's cybersecurity unit reported evidence that a Chinese AI-enabled penetration testing tool called Artex had been used in hacks on companies across Japan. A penetration testing tool is software that security teams use to probe systems for weak spots.
What GMO says: TechCrunch reports that the company has not publicly established a link between Artex and the Onamae breach.
The wider picture: TechCrunch says Artex was also used against South Korean financial institutions in September, according to a CrowdStrike report. The attacks largely relied on weak security, such as a missing second login step called multi-factor authentication. Reuters reported that the tool's developer stopped public updates and closed the source code after it was tied to attacks on banks.
Japan's Financial Services Agency told TechCrunch it issued guidance in May urging financial firms to prepare for more vulnerabilities. It called for stronger basic defenses, including vulnerability management, layered protection and incident preparedness.
What do we still not know?
Several important answers are missing, and the sources we read say so.
- Is the leaked data real? GMO is still verifying it. TechCrunch says the full extent of the incident remains unclear.
- How did the attacker get in? The company has not explained it in the reports we read.
- How many customers lost money? GMO and ASCII.jp say some customers reported unauthorized operations on their trading accounts. No total has been given.
- When will the service return? BleepingComputer says no restart date has been provided for the Desktop Cloud plans.
TechCrunch also says a GMO spokesperson did not answer its request for comment. We will update this story when the company shares more.
What it means for you
- If you use Onamae Desktop Cloud: change your trading-tool and trading-account passwords from another device, log out and check your account history.
- If you trade through a firm like OANDA: turn on two-factor authentication and read their notices.
- If you get an email about the breach: treat it with suspicion. GMO says it will never ask for your password by email or phone.
- If you run your own cloud server: keep secrets such as passwords out of it where you can, and use two-factor login.
The bottom line
GMO Internet says an attacker broke into its cloud desktop service, demanded about $50 million and has now posted data. The company refuses to pay and is checking whether the leaked data is real.
Payment details were not exposed, but trading logins may have been. Customers should change passwords now and keep an eye on their accounts.
Key facts
- Service hit
- Onamae Desktop Cloud, run by GMO Internet
- Servers possibly affected
- Up to 26,739
- Ransom demanded
- About 8 billion yen (about $50 million), not paid
- Compensation offered
- 5,000 yen (about $30) per customer
- Payment data
- Not exposed, GMO says
Got questions?
Quick answers, plain wordsWhat happened to GMO Internet?
GMO Internet says someone gained unauthorized access to its Onamae Desktop Cloud service and installed malicious programs in some customers' server environments. On October 27 it said an attacker had posted information that appears linked to the company and its customers.
What is Onamae Desktop Cloud?
It is a cloud desktop service that gives customers a Windows computer in a data center. BleepingComputer says it is advertised for stable automated currency trading, including running MetaTrader 4, a popular trading program.
How many servers could be affected?
Up to 26,739 customer servers may have had malicious programs installed, BleepingComputer reports. TechCrunch rounds this to 27,000.
Was payment information stolen?
GMO says no. It says payment details such as credit card numbers were not affected because they are stored on separate infrastructure.
What data may have been exposed?
GMO says MetaTrader 4 and MetaTrader 5 credentials and trading-account details stored on the servers may have been exposed or misused. Customers also reported unauthorized operations on their trading accounts.
Did GMO pay the ransom?
No. The attacker demanded about 8 billion yen (roughly $50 million). GMO says it refuses to pay.
What should customers do?
GMO urges customers to reset passwords for their trading tools and trading accounts from a device other than the affected server, and to log off active sessions. Customers should also check their transaction history and watch for phishing emails.
Is this linked to the Artex hacking tool?
Not publicly. About a week earlier, GMO's cybersecurity unit reported that a Chinese AI-enabled testing tool called Artex had been used in hacks on companies across Japan. TechCrunch says GMO has not publicly connected Artex to the Onamae breach.
Will customers be compensated?
GMO says it will pay each customer 5,000 yen (about $30) for the inconvenience, BleepingComputer reports. It says it will consider more compensation for customers whose information was exposed.
SourcesTechCrunch
Topics and tagsCybersecurity, gmo internet, data breach, ransomware
Related stories
UK Legal Aid Agency hackers took records going back to 1978
Eighteen months after the attack, the Ministry of Justice says about 250,000 stolen Legal Aid Agency records predate 2007, and some probation data was taken too.
Rapidus signs up 17 design firms to find customers for its 2nm chips
Japan's state-backed chipmaker launched Rapidus CORE, a partner network including Synopsys, Cadence and Infosys, to help customers design chips it can build.
Arizona court hack exposed data on 1.3 million people after one phishing click
A phishing link opened by a court employee let attackers copy backups with Social Security numbers, protective order records and foster care reports.
More in brief
- Discord will let Google show messages from its biggest public serversOct 28
- Firefox's Smart Window can now fill forms from your open tabsOct 27
- Microsoft offers 60,000 employees a voluntary exit packageOct 27
- Apple's new iMac gets the M6 chip, Wi-Fi 7 and a $1,499 starting priceOct 27
- Turo will let renters filter for Teslas with Full Self-DrivingOct 26
- Meta launches a $35 billion stock sale and plans $60 billion more for AIOct 26