
Technology·News & analysis
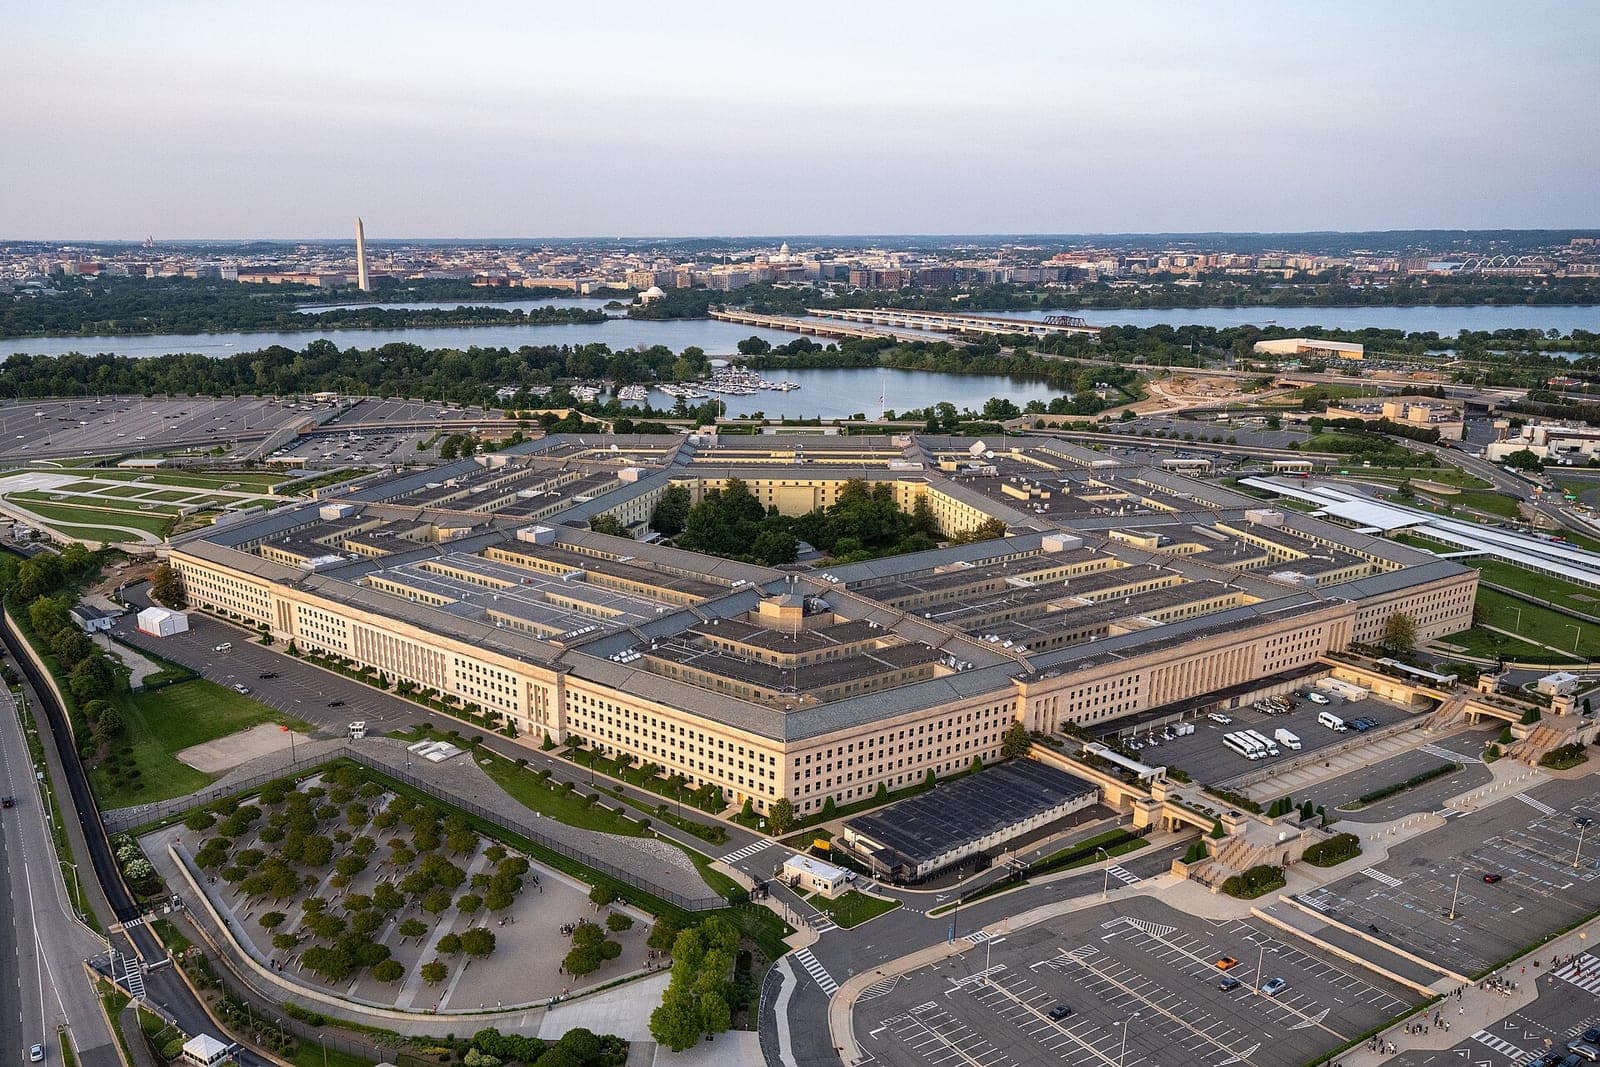
A Pentagon records system was breached for 9 months before anyone noticed
The Defense Manpower Data Center disclosed that unauthorized users accessed unencrypted personal data on 2.76 million living and 294,000 deceased people between October 2025 and July 2026.
Tide
Wave
Sci-fi
1/10
Reality
Shipping
No AI here, just a file-sharing bug nobody caught for nine months.How we rate
The Pentagon's Defense Manpower Data Center disclosed that unauthorized users had access to unencrypted personal data, including Social Security numbers, on 2.76 million living people and 294,000 deceased individuals for roughly nine months before the breach was discovered in July 2026.
It's one of the largest breaches of military personnel data in recent memory, arriving amid a string of federal breaches disclosed in 2026. Anyone who served in the military, worked as a DoD civilian, or has family on file needs to check whether they were affected.
What to know
- The Defense Manpower Data Center (DMDC), which maintains records for more than 60 million current and former military personnel, civilians, and family members, disclosed a data breach in a letter dated September 18.
- Unauthorized users exploited a vulnerability in a DMDC file-sharing system to access unencrypted personal data between October 2025 and July 16, 2026, when the breach was discovered and the vulnerability patched.
- The breach affected roughly 2.76 million living people and about 294,000 deceased individuals, exposing Social Security numbers, names, dates of birth, demographic and contact information, and military service details.
- DMDC says it has found no indication the exposed information has been misused, and is offering affected individuals one year of free credit monitoring and identity-restoration services through IDX.
- This is one of several federal data breaches disclosed in 2026, following a separate FBI jobs website breach attributed to the hacking group ShinyHunters.
A Pentagon system holding records on more than 60 million people sat breached for roughly nine months before anyone noticed, and the personal data exposed included unencrypted Social Security numbers.
What exactly happened, and who's affected?
The Defense Manpower Data Center (DMDC), the Pentagon records-keeping unit that maintains data on current and former military personnel, civilians, contractors, veterans, and family members, disclosed the breach in a notification letter dated September 18. Unauthorized users exploited a vulnerability in a DMDC file-sharing system to access files on a server containing unencrypted personal information.
Why it matters: the breach affected roughly 2.76 million living individuals and about 294,000 deceased people, out of a database covering more than 60 million people total. The exposed data included Social Security numbers, names, dates of birth, demographic and contact information, and military service details, exactly the kind of information used to commit identity theft.
How long did this actually go undetected?
The unauthorized access ran from October 2025 to July 16, 2026, the date DMDC discovered the vulnerability, patched the file-sharing system, and began its formal incident response process. That's roughly nine months of unauthorized access before anyone at DMDC caught it.
Why it matters: a breach window that long means whoever had access had an extended period to potentially copy, export, or otherwise misuse the data before the agency even knew anything was wrong, regardless of what DMDC's current assessment of actual misuse concludes.
Does the Pentagon know who did this, or what's happened to the data since?
No attribution has been made public. The Department of Defense hasn't named a specific individual, group, or nation-state responsible for the unauthorized access. In its notification letter, DMDC stated there has "been no indication of misuse of the recipient's information," though the agency hasn't detailed exactly how that determination was made or how ongoing misuse would be detected.
In real life it's the difference between a bank telling you "we don't see anything," and a bank actually walking you through how they're watching your account for the fraud that data like this typically enables months or years later, not just in the days right after a breach becomes public.
What is DMDC actually offering affected people?
DMDC is providing one year of free credit monitoring and identity-restoration services through IDX, a contracted identity protection firm. Affected individuals with questions were directed to contact IDX directly through its dedicated response portal or by phone.
- Credit monitoring and identity restoration: one year, free, through IDX.
- Contact: response.idx.us/DMDC, or by phone for those who received a notification letter.
- Who should act: anyone who received DMDC's September 18 letter, or who believes their DMDC-held records may have been included.
Why it matters: one year of credit monitoring is a standard offering after breaches like this, but Social Security numbers and full personal profiles don't expire after twelve months. Identity thieves who obtain this kind of data sometimes wait well beyond a standard monitoring period before actually using it, a pattern security researchers have observed across past large-scale breaches.
What does DMDC actually do, and why does a breach there matter so much?
Background: DMDC administers the Defense Enrollment Eligibility Reporting System (DEERS), a computerized database covering current and former service members, military retirees, disabled veterans, dependents, and DoD contractors worldwide. DEERS is the backbone behind military healthcare eligibility through TRICARE, educational and life insurance benefits, and identity verification across the Department of Defense.
DEERS also underpins the Common Access Card (CAC), the physical ID badge that grants military personnel access to bases, secure systems, and benefits, each tied to a unique electronic identifier stored in DEERS. In practical terms, DMDC's systems are the infrastructure that confirms someone actually is who they claim to be within the military benefits and access system.
Why it matters: a breach at the agency responsible for that identity backbone carries more weight than a typical consumer data leak. The exposed Social Security numbers and personal details are the same identifiers used to verify identity, eligibility, and access across military healthcare, benefits, and base security systems, not just financial accounts, which is part of why credit monitoring alone may not fully address the risk this specific breach creates for affected individuals.
Is this part of a bigger pattern this year?
Background: this is one of several federal data breaches disclosed throughout 2026. In late September, the hacking group ShinyHunters claimed it breached the FBI's own jobs portal, FBIJobs.gov, exploiting a previously unknown vulnerability in Oracle's PeopleSoft software.
The group claimed to have stolen 2 to 3 terabytes of employee data, including full names, home addresses, dates of birth, and Social Security numbers, with a 5,000-record sample shared as proof. The FBI confirmed it was handling a "cybersecurity incident" on September 26, without immediately confirming the full scope ShinyHunters claimed.
Separately, an unrelated breach this year exposed more than 153 million driver's license records across the US, and a Florida DMV breach exposed roughly 200,000 state identification records. Security researchers have also pointed back to the 2015 breach of the Office of Personnel Management (OPM), which exposed background-check data on more than 21 million federal employees, as a longer-running historical reference point for breaches of this scale hitting government personnel systems specifically.
That 2015 OPM breach, widely attributed to state-sponsored hackers, is still cited today as one of the most consequential government data breaches in US history, given how extensively background-check data can be used for espionage and targeting purposes well beyond ordinary identity theft.
Why it matters: taken together, these incidents point to a pattern of federal and government-adjacent systems struggling to keep pace with the security demands of the personal data they hold, even as the scale and sensitivity of that data keeps growing. A nine-month undetected breach at an agency responsible for tens of millions of records suggests detection capabilities, not just prevention, remain a real gap.
What it means for you
- If you served in the US military, worked as a DoD civilian, or are a family member on file with DMDC, check whether you received a notification letter. If you did, sign up for the free IDX credit monitoring promptly.
- Watch for signs of identity theft even after enrolling in monitoring, unfamiliar credit inquiries, new accounts you didn't open, or unexpected government correspondence, since Social Security numbers don't expire the way a monitoring subscription does.
- This breach also affected deceased individuals' records. If you manage the affairs of a deceased family member who may have been in DMDC's system, it's worth checking on their behalf too.
- Treat any unsolicited contact referencing this breach with caution. Scammers frequently use real breach news to run phishing attempts claiming to offer "help" with compromised accounts.
The bottom line
A nine-month gap between when unauthorized access began and when it was actually discovered is the most concerning detail in this breach, not just the raw number of records exposed.
For the millions of people affected, the practical next step is straightforward: enroll in the credit monitoring DMDC is offering and stay alert for identity theft warning signs well beyond the one-year coverage window, since data this sensitive doesn't become less valuable to criminals once a monitoring subscription runs out.
Key facts
- Records agency
- Defense Manpower Data Center (DMDC)
- People affected
- 2.76M living, 294K deceased
- Breach window
- October 2025 to July 16, 2026
- Data exposed
- SSNs, names, DOBs, service records
- Offered remedy
- 1 year free credit monitoring (IDX)
Got questions?
Quick answers, plain wordsWhat is the Defense Manpower Data Center, and why does it matter here?
DMDC is a Pentagon records-keeping unit that maintains data on more than 60 million people, including current and former military personnel, civilian employees, contractors, veterans, and family members, making it one of the largest personnel databases in the US government.
How many people were actually affected by this breach?
About 2.76 million living individuals and roughly 294,000 deceased people, based on figures DMDC provided in its September 18 notification letter.
What information was exposed?
Unencrypted personal data including Social Security numbers, names, dates of birth, demographic and contact information, and military service details, according to DMDC's breach notification.
How long did the breach last before it was discovered?
Unauthorized access occurred between October 2025 and July 16, 2026, when DMDC discovered a vulnerability in its file-sharing system, patched it, and began its incident response process, meaning the exposure went undetected for roughly nine months.
How did the breach actually happen?
DMDC said a security vulnerability in one of its file-sharing systems allowed a small number of unauthorized users to access files on a server containing unencrypted personal information. The agency hasn't disclosed further technical details about the specific vulnerability.
Do officials know who's behind the breach?
No attribution has been made public. The Department of Defense has not named a specific individual, group, or nation-state responsible for the unauthorized access.
Has any of the exposed information actually been misused?
DMDC said in its notification letter that there has been no indication the accessed information has been misused, though it hasn't detailed how that determination was reached or how it would detect misuse going forward.
What is DMDC offering affected individuals?
One year of free credit monitoring and identity-restoration services through IDX, a contracted identity protection firm. Affected individuals with questions were directed to contact IDX directly at response.idx.us/DMDC or by phone.
Is this part of a bigger pattern of federal data breaches?
Yes. It's one of several federal breaches disclosed in 2026, including a separate FBI jobs website breach attributed to the hacking group ShinyHunters, that together involved terabytes of stolen data and, in some cases, over a hundred million exposed records across different incidents.
What should someone affected by this breach actually do?
Anyone who received DMDC's notification letter should sign up for the free credit monitoring and identity-restoration services offered through IDX, and watch for signs of identity theft such as unfamiliar credit inquiries or accounts, given that Social Security numbers were among the exposed data.
SourcesDefense Manpower Data Center
Topics and tagsCybersecurity, Data centers, cybersecurity, data breach
Related stories
Dutch police arrest a security professional in the ShinyHunters hacking probe
Police arrested a 24-year-old Amsterdam man working in offensive security on suspicion of ties to ShinyHunters, the group behind some of the largest data breaches in recent years.
Apple's smart home hub reportedly launches October 13, with a camera that never records video
Bloomberg's Mark Gurman says Apple will announce its long-rumored smart home display on October 13. He also describes a companion home camera that sends text descriptions instead of video.
GrayKey maker reportedly found a way around the iPhone's Inactivity Reboot
A leaked training video seen by 404 Media says Magnet Forensics' new tools keep a seized iPhone in an easier-to-search state, even after the reboot Apple added in iOS 18.1.
More in brief
- arXiv limits researchers to two papers a month as AI drives submissions to a recordOct 2
- California will fine robotaxi companies that block first responders for over 30 minutesOct 2
- Microsoft launches real-time transcription and new voice models for AI voice agentsOct 1
- Cloudflare releases Clef, open-weight AI models that make yes-or-no decisions fastOct 1
- Fervo's Cape Station becomes the first enhanced geothermal plant to sell power commerciallyOct 1
- Cloudflare renames its data platform Basin and makes it generally availableOct 1